Every server.One quiet tab.
Console, provisioning, discovery and rack-level control for your entire fleet, reachable from one browser tab with nothing exposed to the network.
The way in is the weakest door.
iDRAC, iLO and IPMI were never built for the open network. VPNs, port-forwards and shared passwords turn the management plane into the widest door in the building. Tengan closes it.
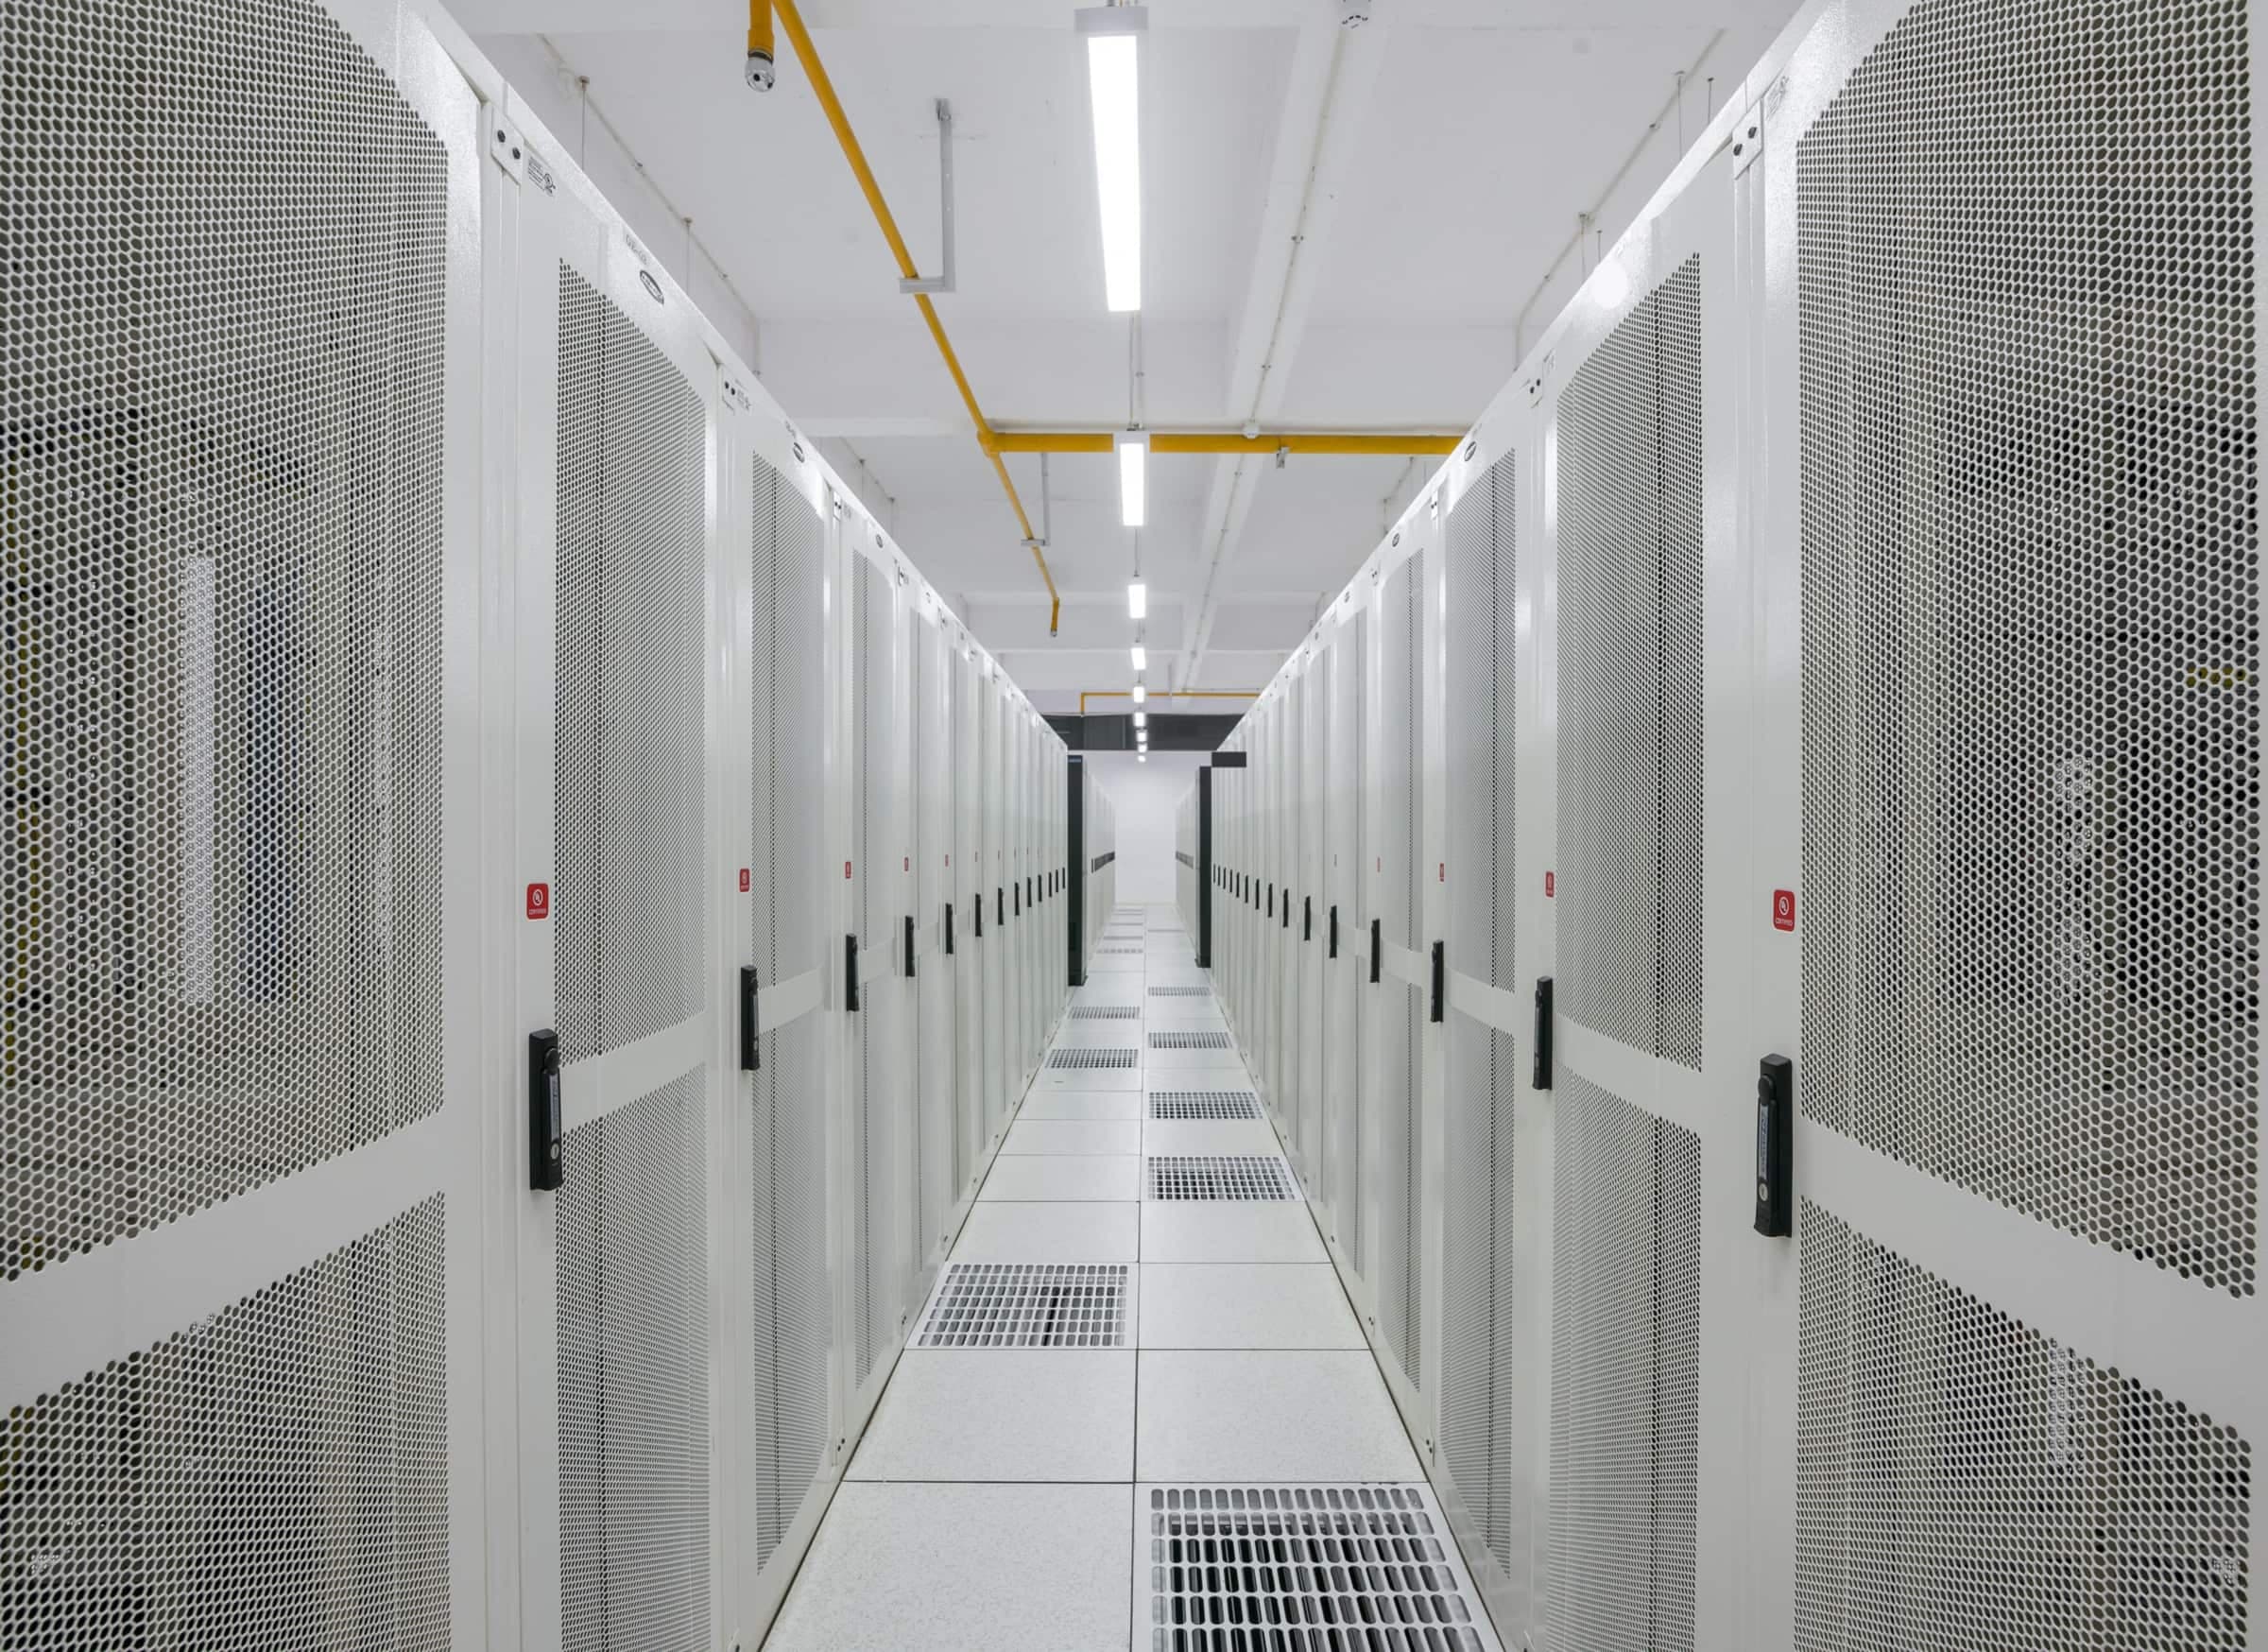
Every rack, without walking the aisle.
Consoles, power and health for the whole hall, reached from one browser tab.
Nothing touches the server.
Open a tab and Tengan brokers an encrypted, authenticated path to the controller, then closes it. Nothing is left listening: no persistent tunnels, no open ports on the BMC network.
You open a tab.
No client, no VPN, no plugin: any modern browser on any OS. The Smart Proxy handles everything behind the scenes.
Tengan brokers the path.
An encrypted, authenticated tunnel to the BMC, opened on demand and scoped to your session and your permissions only.
Then the door shuts.
The controller is never placed on the network. The path closes the moment your session ends: no port stays open, no address stays reachable.
On demand, never standing
The tunnel exists only for the life of your session. There is nothing to scan, and nothing to exploit between sessions.
Scoped to you
Every path is bound to the authenticated operator and their RBAC scope, not a shared service account.
Fully brokered
The Smart Proxy terminates the connection; the BMC only ever talks to the proxy, never to the open network.
Full KVM, from the browser.
Keyboard, video and mouse down to the BIOS: no Java applet, no client install, no direct route to the BMC network. Reach any server the moment you open a tab.
Pre-boot
Full KVM down to the BIOS, before the OS loads.
No client
Pure HTML5: no Java, no plugin, any browser.
Every keystroke
Captured in the audit trail, automatically.
Bare metal to booted.
PXE boot, mount ISOs and drive kickstart templates across the fleet. Roll an OS to one node or a hundred in parallel, and watch every machine report back.
One or a hundred
Parallel rollout with live per-host status.
Any recipe
Kickstart, Preseed and cloud-init templates.
A plan, not a weekend
Golden images and per-role profiles, automated.
Built for halls like these.
Rows, cages, odd corners and thousands of nodes. Tengan models the rooms you actually have and reaches every controller in them.
Every link, accounted for
Ports, patches and circuits recorded end to end, so a trace starts in the browser.
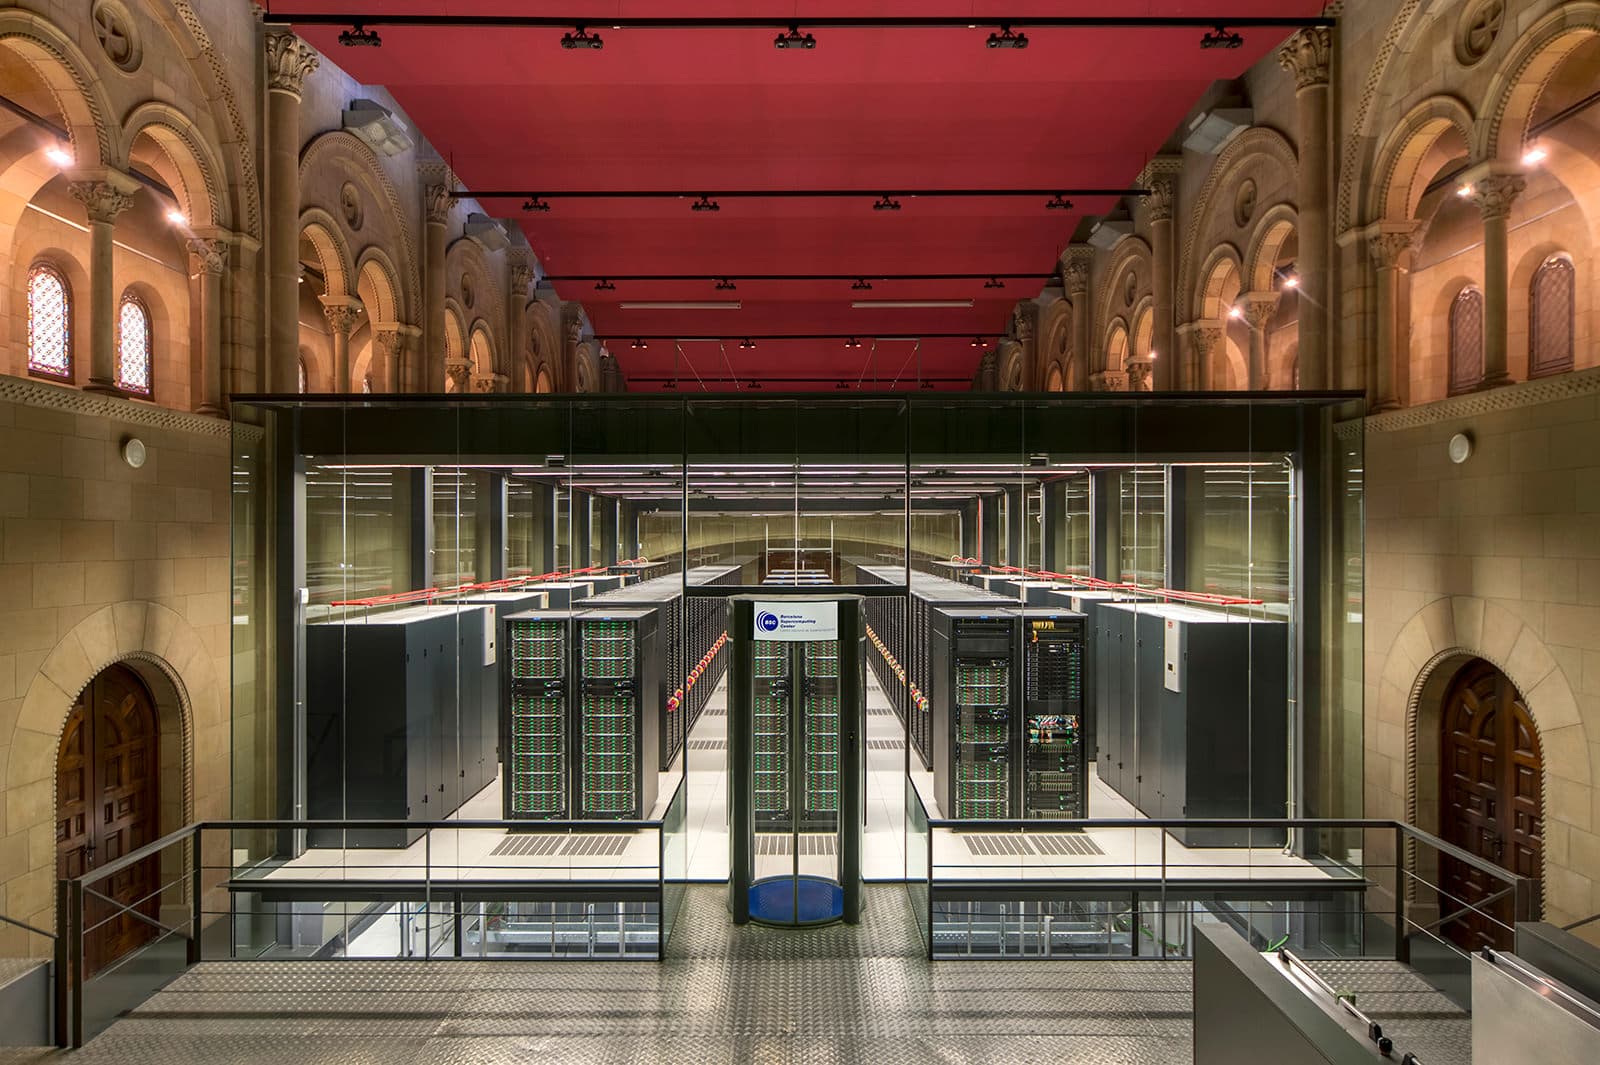
Any building, any floor plan
Model the rooms you actually have: rows, cages and odd corners included.
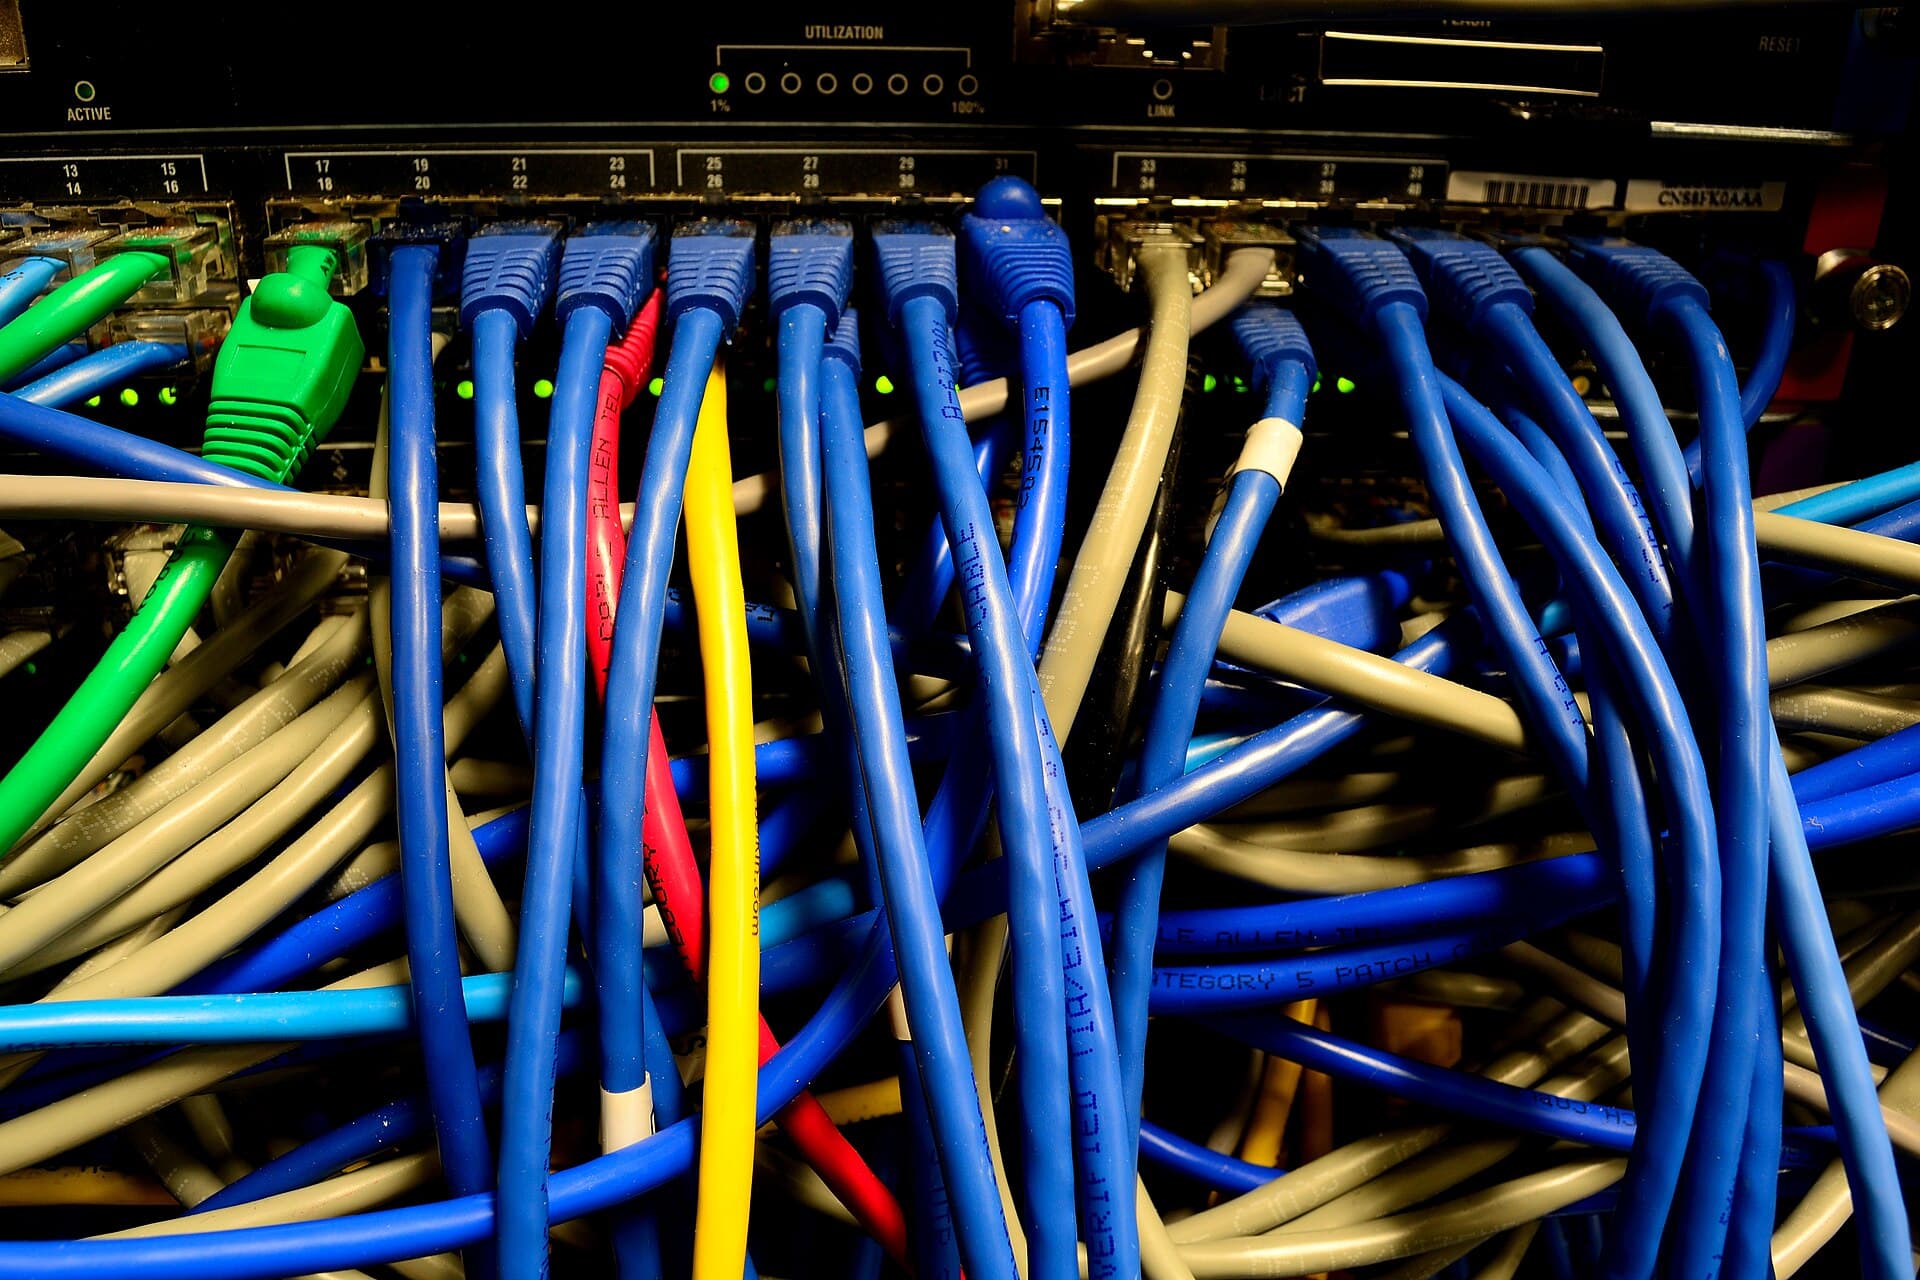
Every port, every patch
Know which cable goes where before anyone opens a cabinet door.
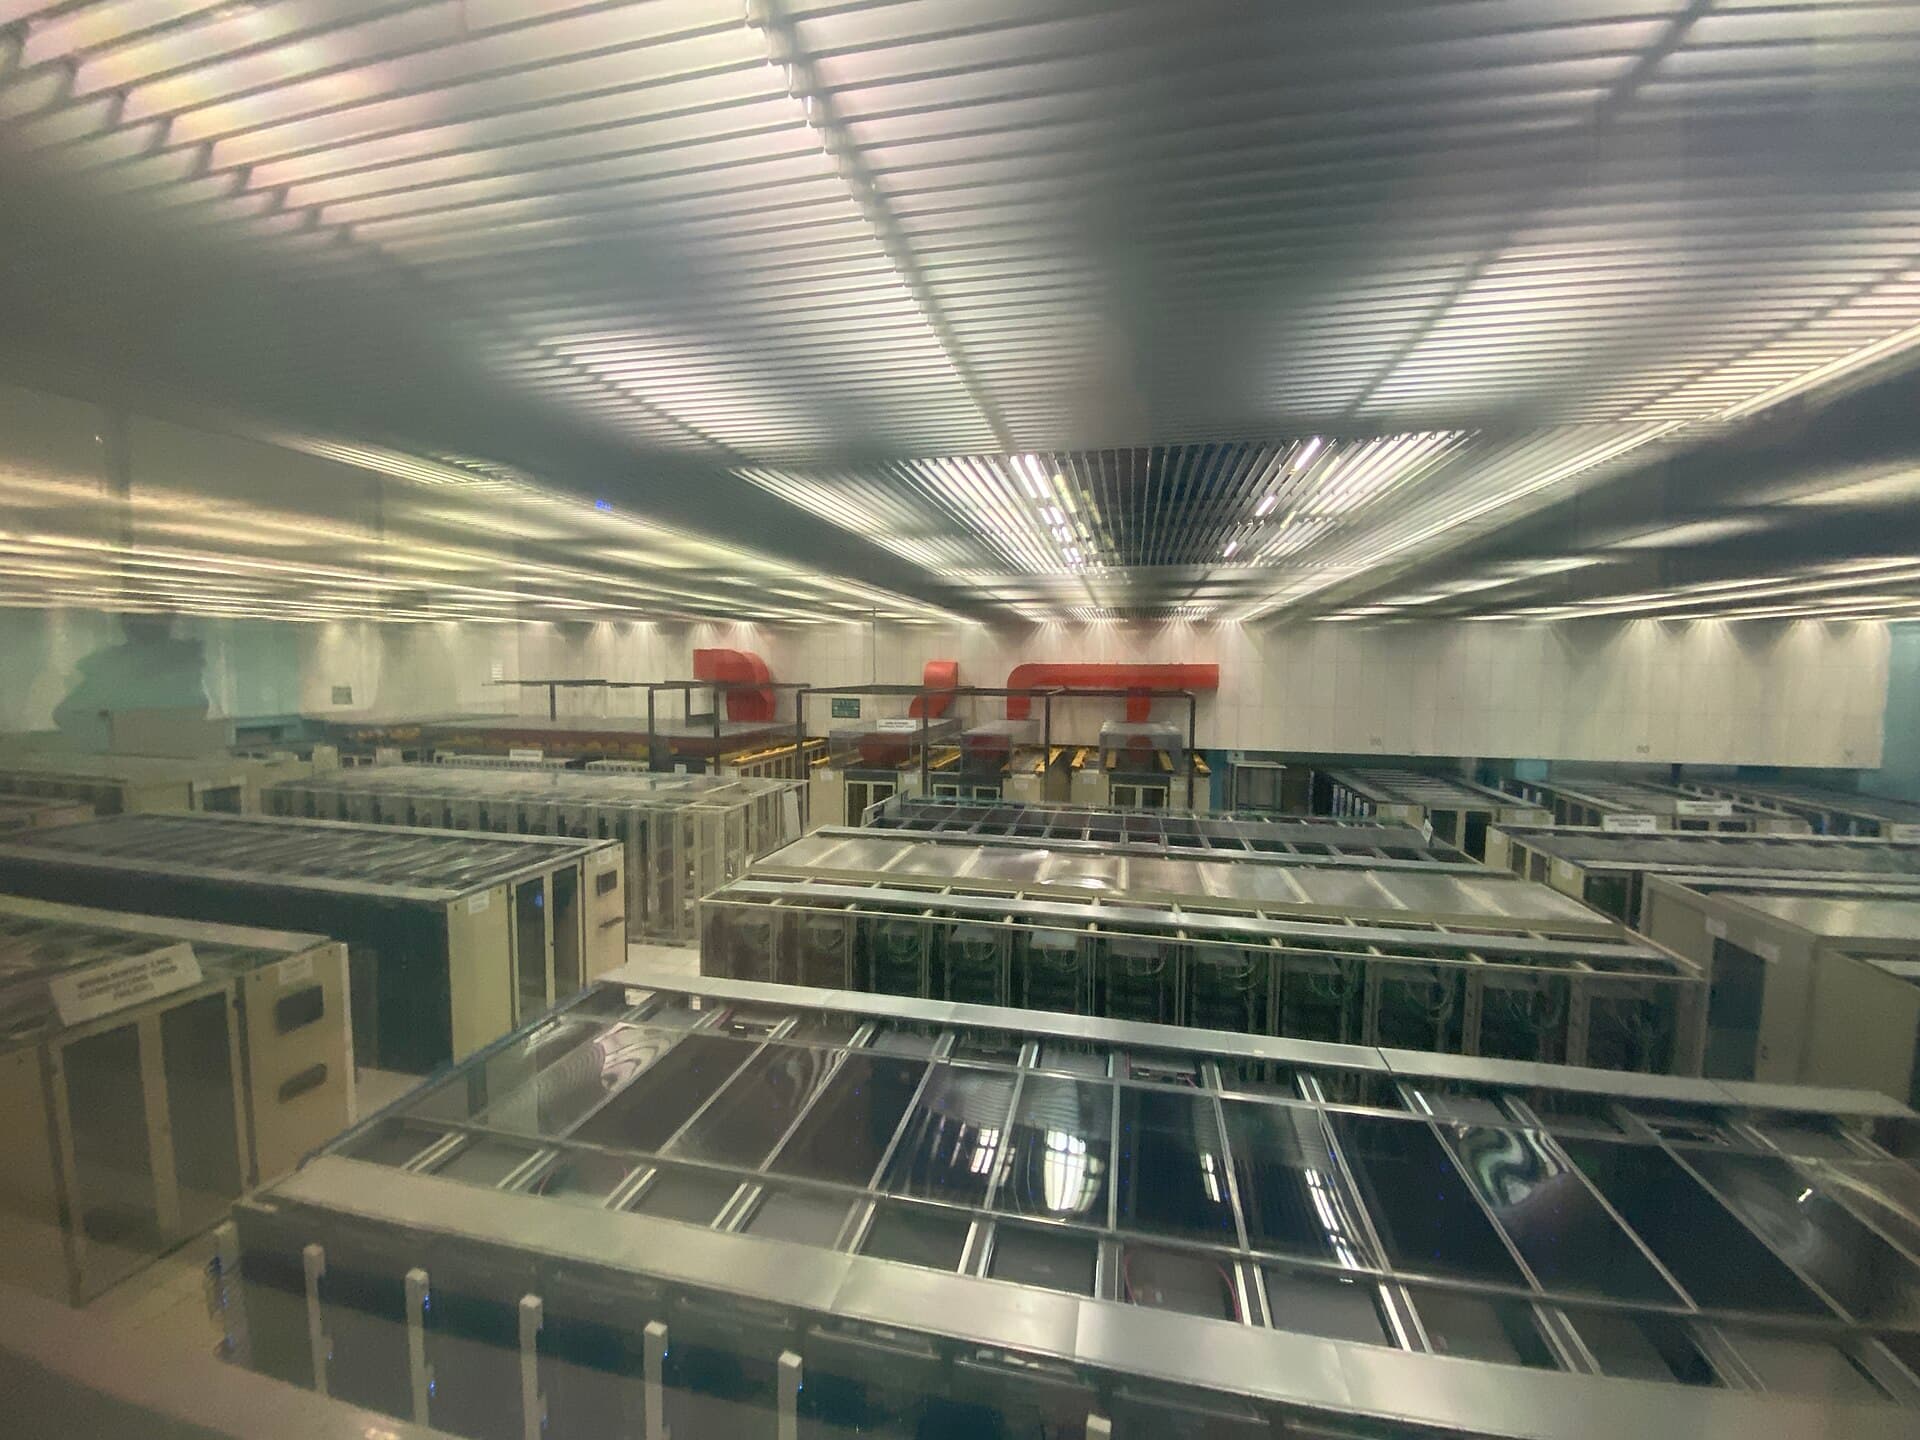
Thousands of nodes, one view
Every controller, its health and its console, without a jump host per rack.
Find what's really there.
Sweep a subnet and Tengan surfaces every controller, including hosts that drop ICMP and answer on no open port. Vendor, model and firmware version are identified automatically, so the inventory builds itself.
ICMP-silent
Found via TCP fingerprinting even when they drop every ping.
Auto-identified
Vendor, model and firmware read without credentials.
Zero agents
Nothing on the host, nothing on the BMC. Pure discovery.
Read the room, not a spreadsheet.
Model the floor, the cabinets, the cabling and the circuits, then read capacity, power and heat straight off the layout instead of reconciling three asset registers by hand.
Floor to U
Rooms, rows, racks and every rack unit in one model.
One click, live
OS, IP, power draw and open sessions per unit.
Power and heat
Draw per circuit and a thermal map across the room.
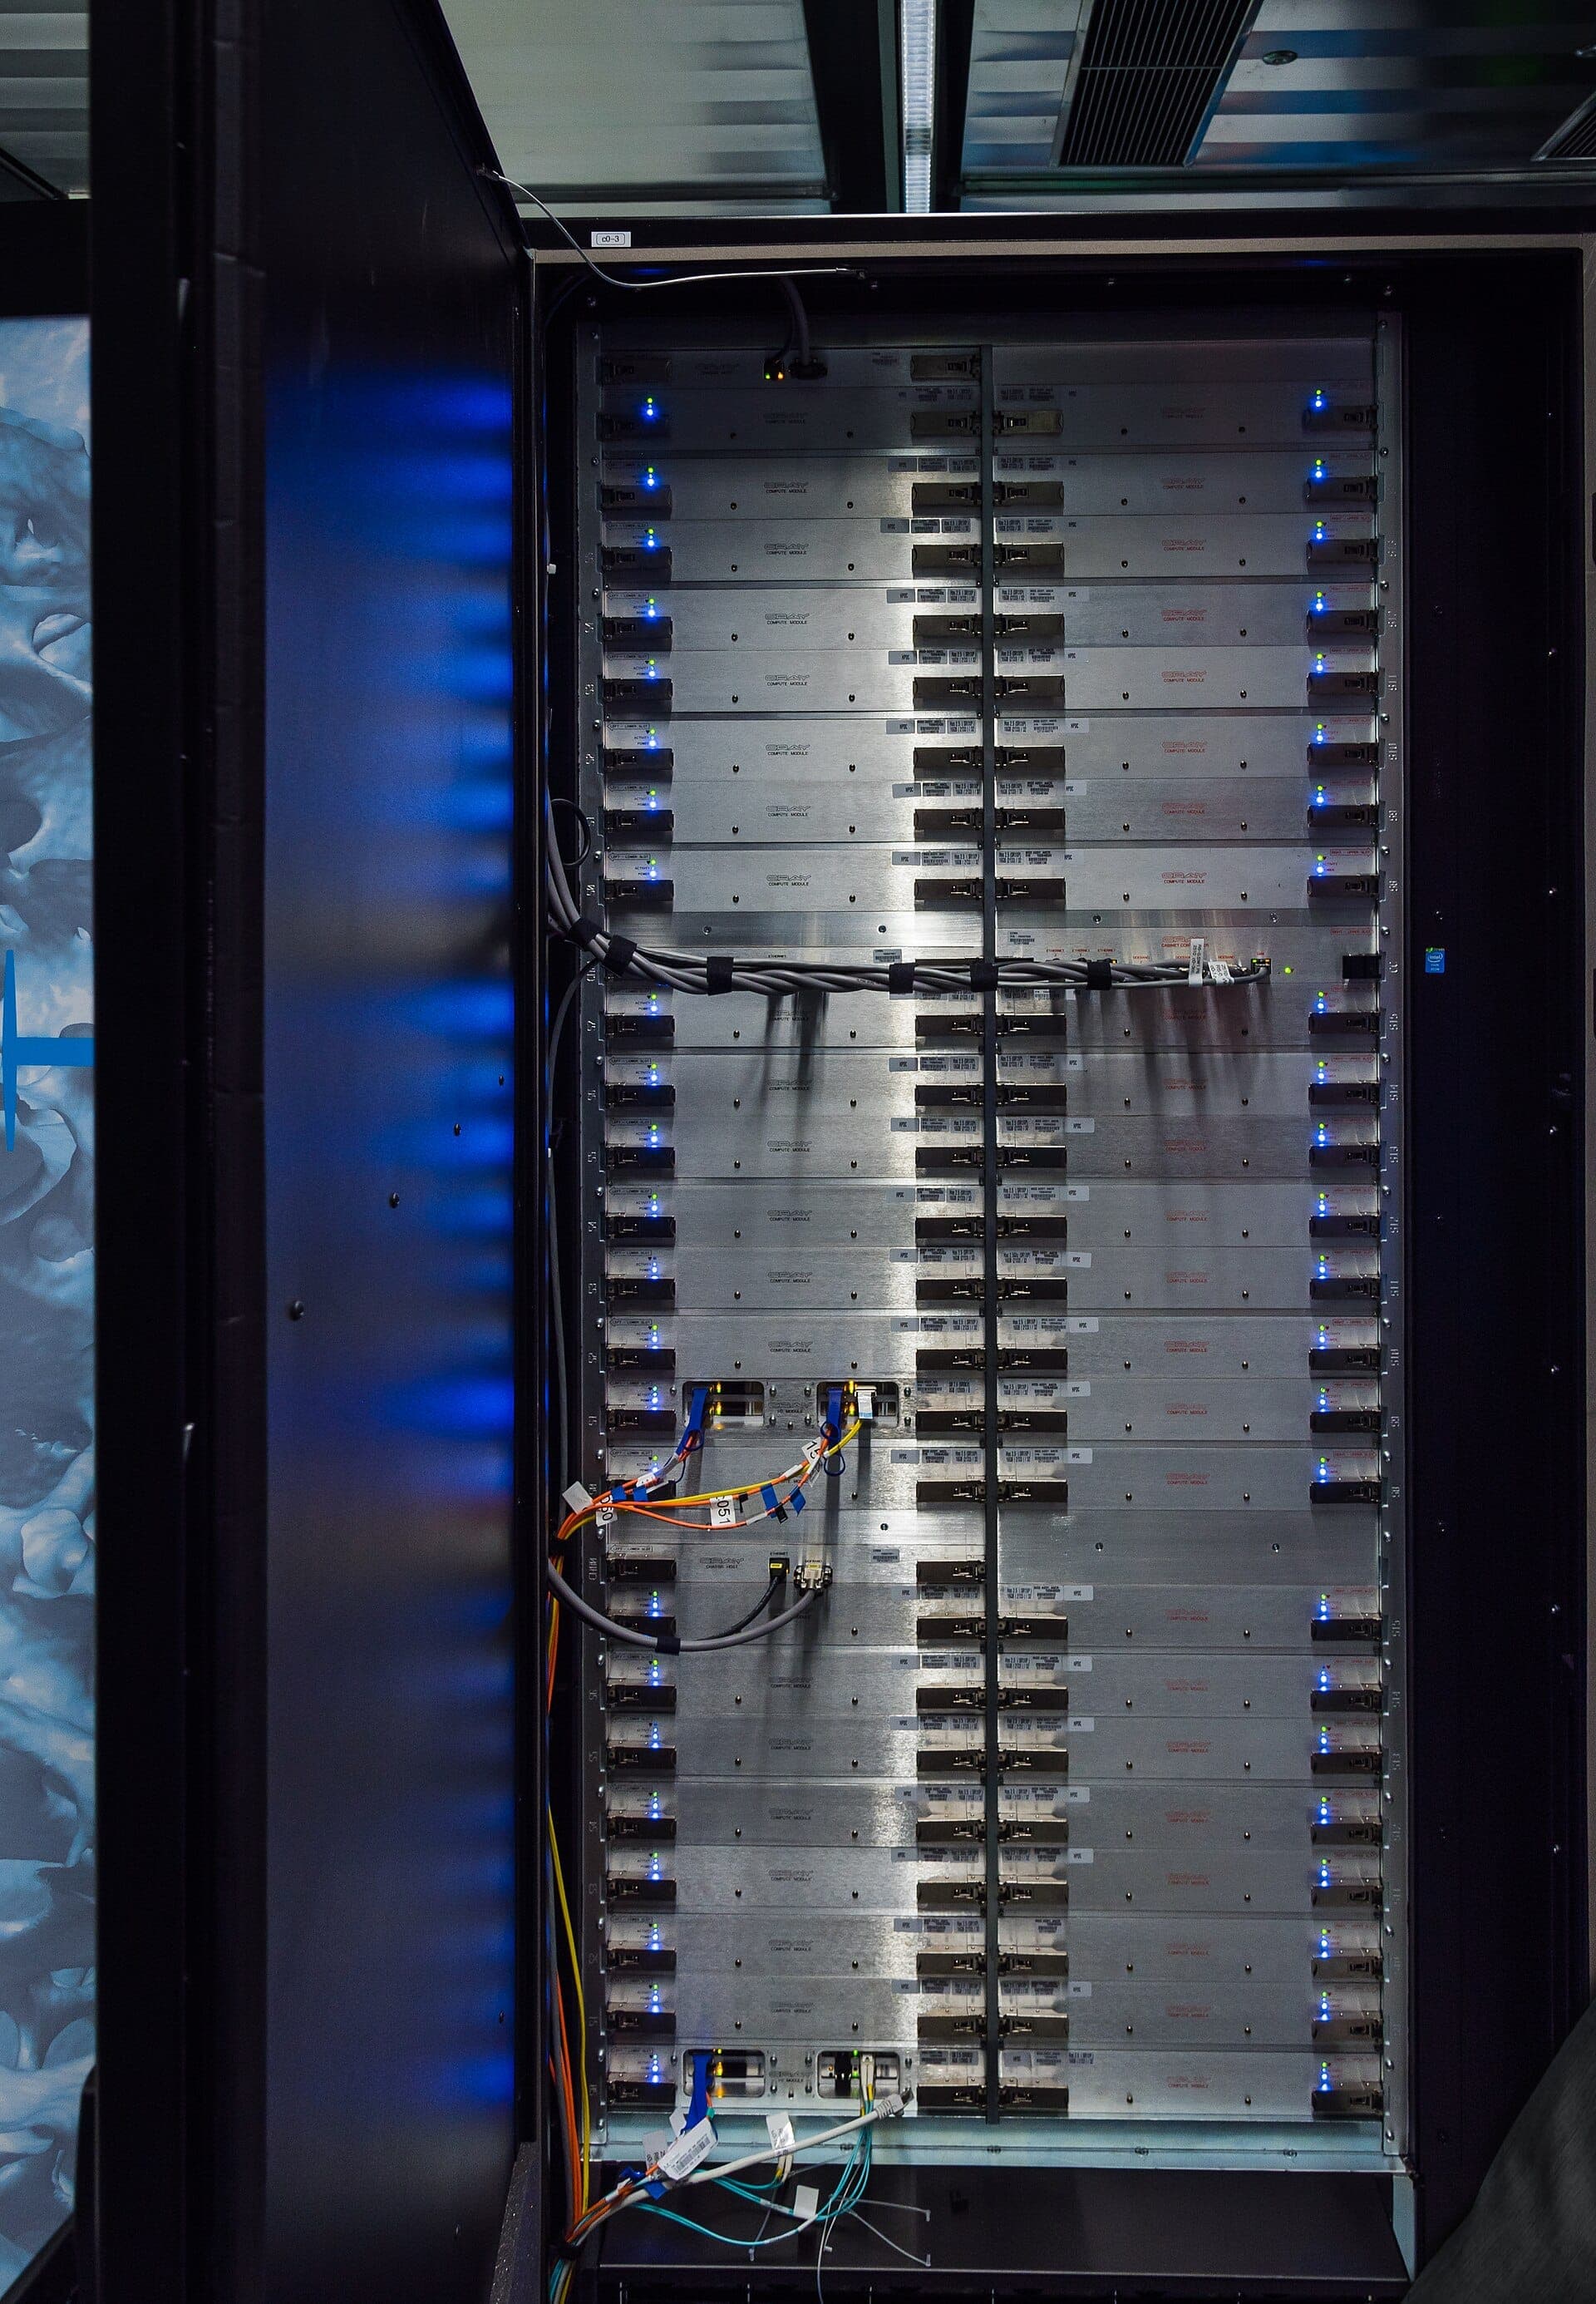
Encrypted end to end.
The path to a controller exists only while you hold it open. Close the tab and it is gone.
Every vendor. Two standards.
Built on DMTF Redfish 1.x and IPMI 2.0: no vendor SDK, no per-fleet integration work. One console speaks to the whole floor.
- 8
server platforms
Dell iDRAC, HPE iLO, Lenovo XClarity, Supermicro, Cisco CIMC, Fujitsu, Huawei and Inspur, all through Redfish or IPMI 2.0.
- 2
open standards
DMTF Redfish 1.x and IPMI 2.0. No proprietary agents, no SDK dependencies, no per-vendor maintenance burden.
- 0
client installs
Browser KVM down to the BIOS: no Java, no plugins, no direct route to the BMC network. Any OS, any browser.
Logged. Sealed. Unexposed.
Every command and change is captured in a tamper-evident audit trail. Credentials live in an AES-256 vault and rotate automatically, so operators connect without ever seeing a password.
Audit trail
Every session logged keystroke by keystroke in a tamper-evident store, replayable and exportable to your SIEM.
Credential vault
AES-256 at rest, rotated on a schedule. Operators connect without ever seeing a password.
Access control
Granular RBAC scoped to host and action, with SAML 2.0, SSO and MFA at the platform level.
Take command.
Deploy on-premise in an afternoon and see Tengan running against your own fleet.
On-premise deployment · Enterprise support · Custom integrations.